
By Matt Busel, who built the apps, crates and game he writes about · every number links to its source and every dataset is downloadable (methods) · corrections · featured in Kirino, gamebiz, This Week in Rust, New Mobile Life, By-Press
Docker is weird, and Rust won't fix it: youki had 3 high escapes
On this page · 9 sections
- Key numbers
- The post that set HN off: containers are 5 kernel features in a trenchcoat
- Receipt one: Docker's runtime smuggles C to dodge Go
- Receipt two: the Rust rewrite shipped the same escapes
- Receipt three: C is not the villain either
- Follow the money: who wins from "Docker is weird"
- Where this goes next
- What this means for you
- Sources
Short answer: Docker is weird because its runtime, runc, is a Go program that needs 1,232 lines of C to run before Go even wakes up. The popular fix people reach for is "rewrite it in Rust", but youki, the Rust runtime, has 4 security advisories on record and 3 of them are high severity: the same count of high-severity escapes runc has shipped since January 2025.
TL;DR: We pulled every GitHub security advisory for the three main OCI container runtimes on Oct 26 2026. Since Jan 1 2025, runc (Go) logged 4 advisories with 3 high, crun (C) logged 6 with 2 high, and youki (Rust) logged 4 with 3 high. Two of youki's high-severity bugs landed on Nov 5 2025, the same day runc disclosed its masked-path and procfs-write escapes, because the bug was in the design both runtimes copied, not in the memory. If you run containers, the language of your runtime matters far less than how fast you patch it.
Key numbers
| What | Number | Source, checked Oct 26 2026 |
|---|---|---|
| youki (Rust) advisories, all time / high | 4 / 3 | GitHub advisories |
| runc (Go) advisories since Jan 2025 / high | 4 / 3 | GitHub advisories |
| crun (C) advisories since Jan 2025 / high | 6 / 2 | GitHub advisories |
| Lines of C in runc's nsexec.c | 1,232 | runc source |
| Docker Hub pulls of the ubuntu image | 10.1 billion | Docker Hub API |
| GitHub stars: moby vs youki | 72,211 vs 7,654 | GitHub API |
The post that set HN off: containers are 5 kernel features in a trenchcoat
On Oct 22 the blog Code and Cake posted "Docker is weird", a write-up from someone building their own container runtime for fun. It hit 876 points and 366 comments on Hacker News.
The core points land hard. Containers are not a thing the kernel knows about; they are a normal process wrapped in namespaces (what it can see), cgroups (how much it can use) and a pile of network plumbing. An image is a folder that Docker drops somewhere and then chroots into.
And the spiciest line: Go is "kind of a terrible language for a container runtime". Go starts many threads on its own, and a lot of the Linux calls a runtime needs only work from a single thread. Go also has no real fork.
Receipt one: Docker's runtime smuggles C to dodge Go
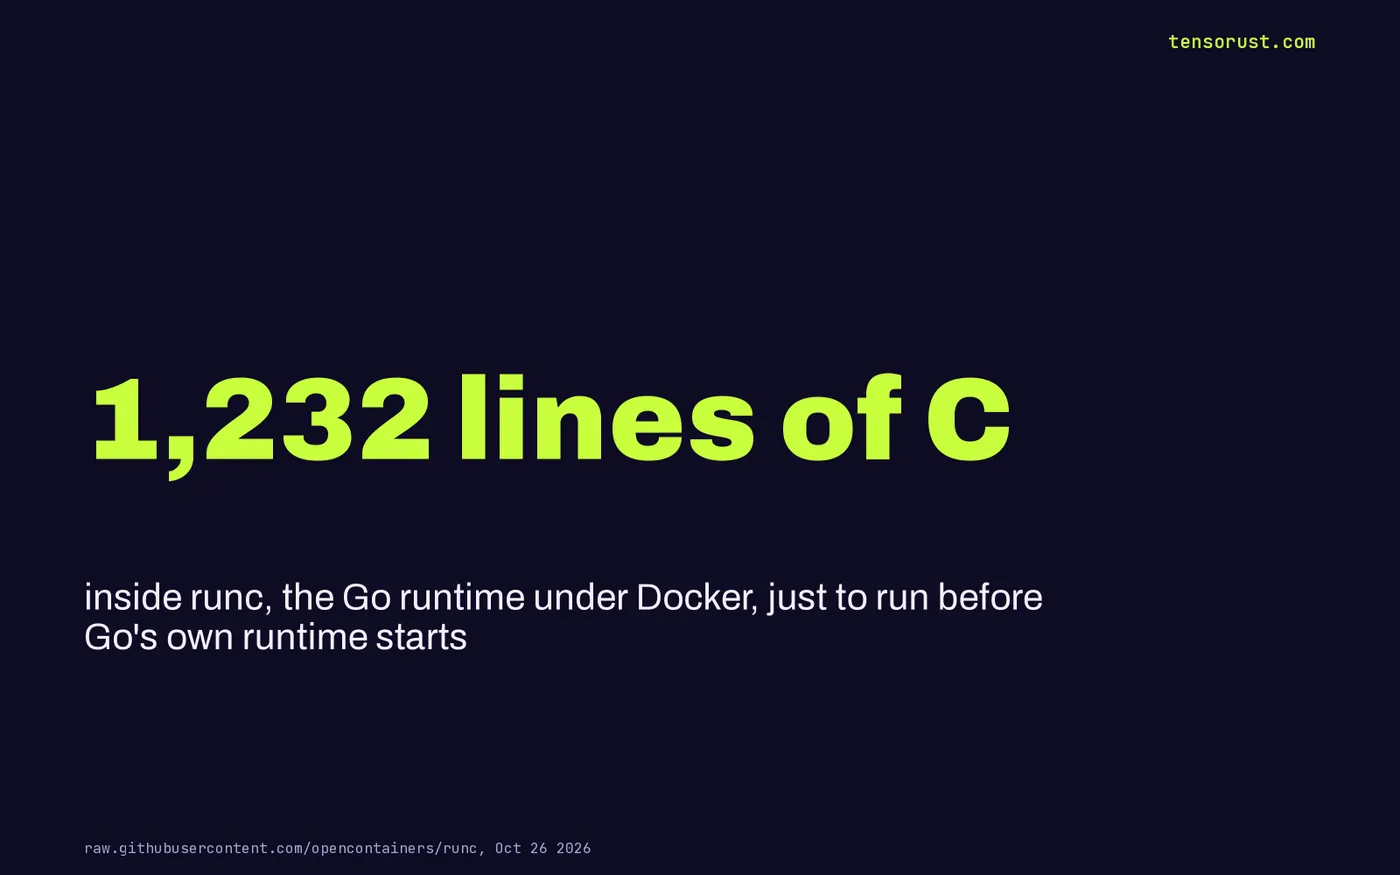
The author is right, and the source proves it. runc, the runtime under Docker, containerd and Kubernetes, ships nsexec.c: 1,232 lines of C (we counted the file on Oct 26) that run before the Go runtime starts, just to do the namespace setup Go can't do safely.
Then runc re-executes itself through /proc/self/exe to fake a fork. That is the "weird" in Docker is weird: the most-pulled software stack on earth (the ubuntu image alone has 10.1 billion Docker Hub pulls, alpine 12.4 billion) runs on a Go program wearing a C mask.
Receipt two: the Rust rewrite shipped the same escapes
So the obvious r/rust answer is youki, a container runtime written in Rust with no Go runtime to fight. It is real, it is maintained (106 commits in the last 90 days), and its libcontainer crate has 137,368 downloads on crates.io.
Here is the part the rewrite-it-in-Rust crowd skips. youki has 4 security advisories on GitHub. 3 are rated high. That is 75% of its record, and it matches runc's 3 high-severity advisories since January 2025 one for one.
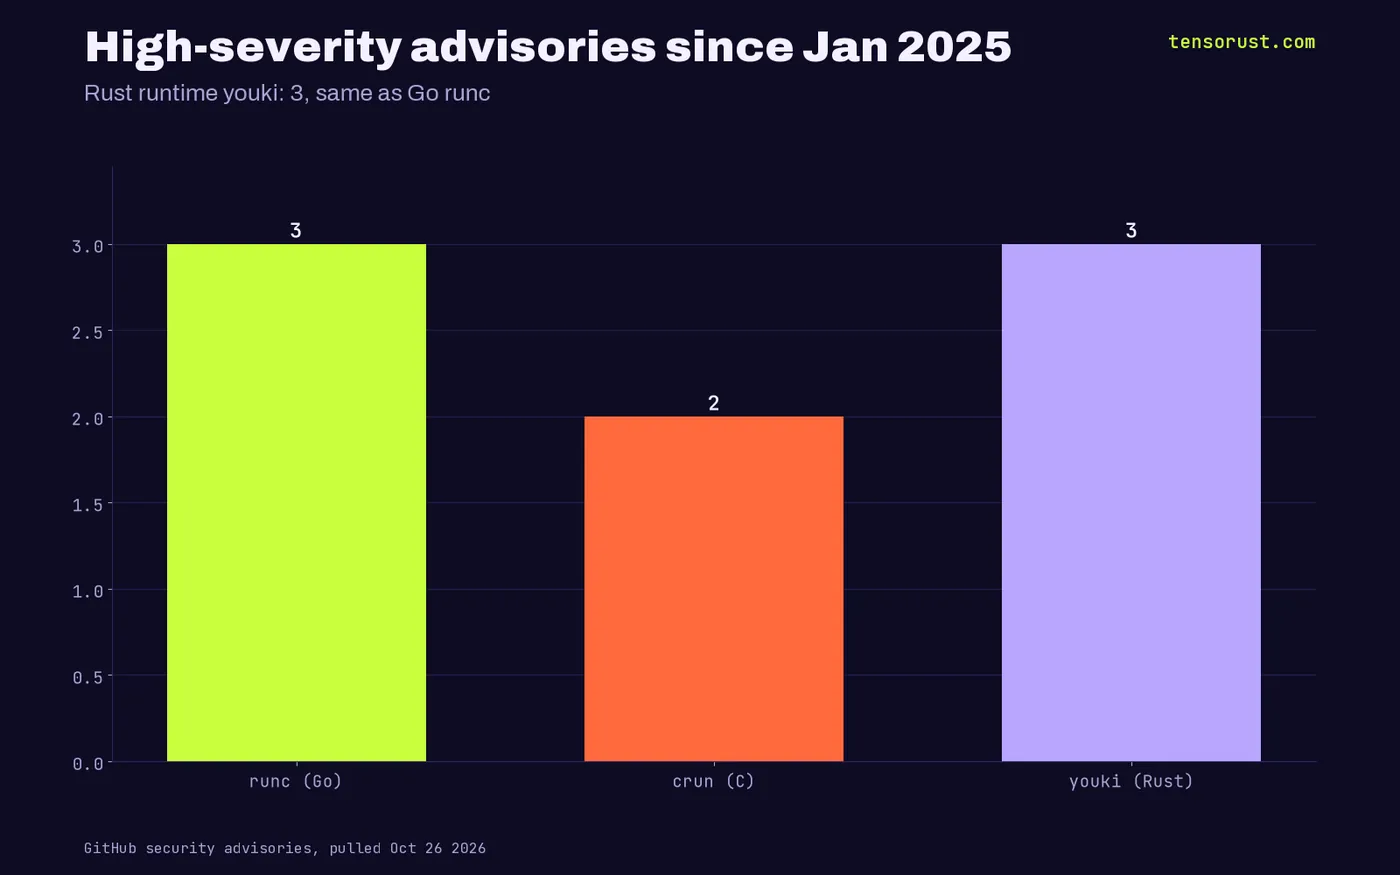
Look at the dates. On Nov 5 2025 runc published container escape via "masked path" abuse due to mount race conditions and an escape via arbitrary write gadgets and procfs write redirects. The same day, youki published advisories with word-for-word the same titles (GHSA-vf95-55w6-qmrf and GHSA-4g74-7cff-xcv8).
No buffer overflow, no use-after-free. These are races and symlink tricks on /proc, /dev and mount points. Rust's borrow checker protects memory. It does not know what a mount namespace is, and it can't stop a malicious image from swapping a path between your check and your use (a "TOCTOU" race: time of check vs time of use).
Receipt three: C is not the villain either
crun, Red Hat's runtime written in plain C, logged 6 advisories since 2025, the most of the three, but only 2 high. Several are the same family: crun following a /dev or /dev/console symlink planted by the container image.
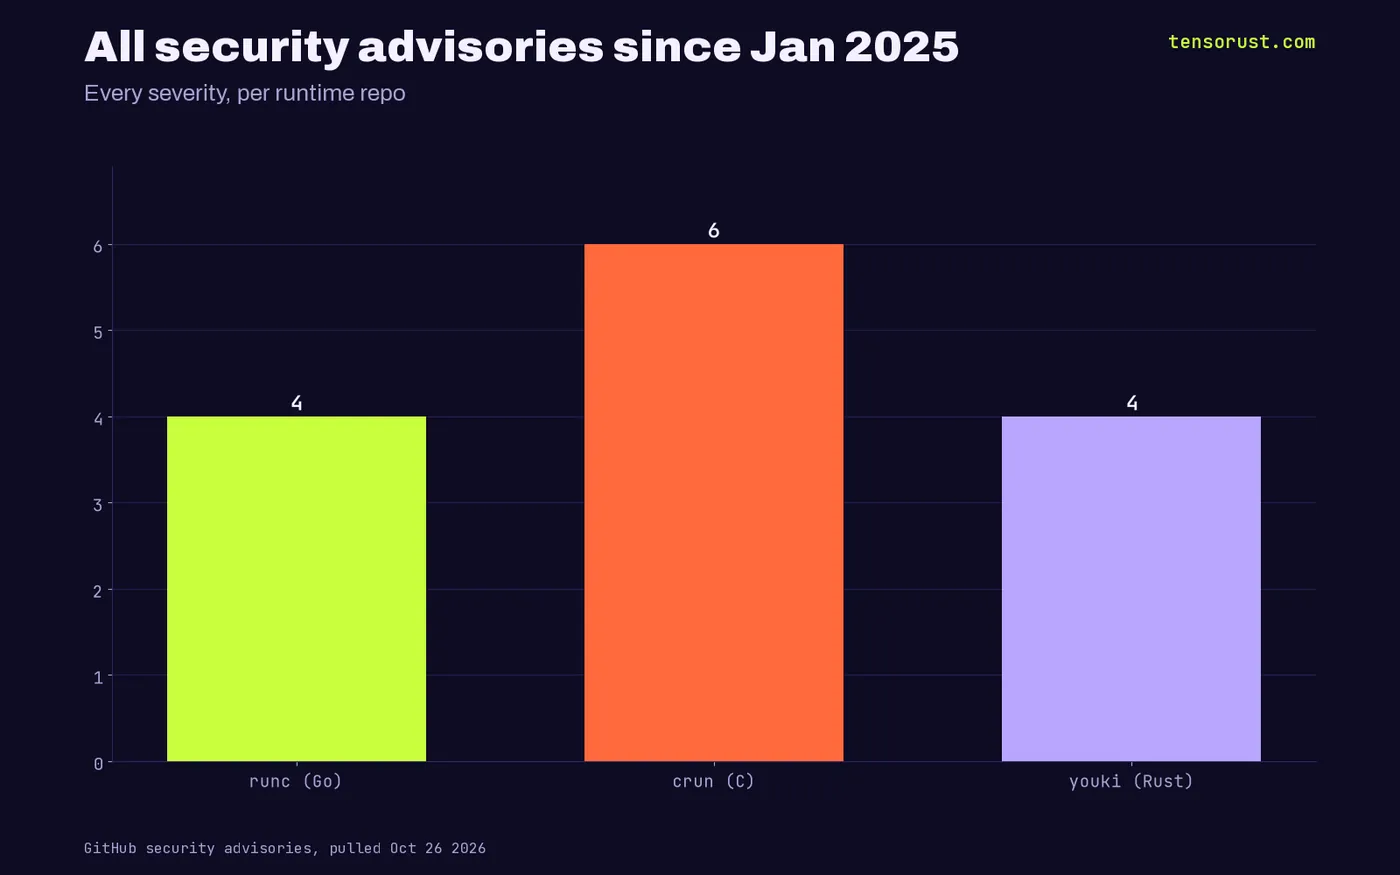
All three runtimes, in three languages, keep tripping over the same Linux surface. Our read: the bug class lives in the kernel API, not the compiler. Anyone selling a language as the cure for container escapes is selling vibes, and that includes our own Rust lane.
Follow the money: who wins from "Docker is weird"
Docker Inc wins from the weirdness staying hidden. Docker Desktop is the paid product, and its whole pitch is that you never have to see runc, cgroups or /proc/self/exe. The weirder the guts, the more a nice wrapper is worth.
Podman, backed by Red Hat, wins from the rootless story: 33,122 GitHub stars, almost half of moby's 72,211, sold on "no root daemon". The Code and Cake post nails the catch: rootless networking has to rebuild the network stack in userspace, so you trade one kind of weird for another.
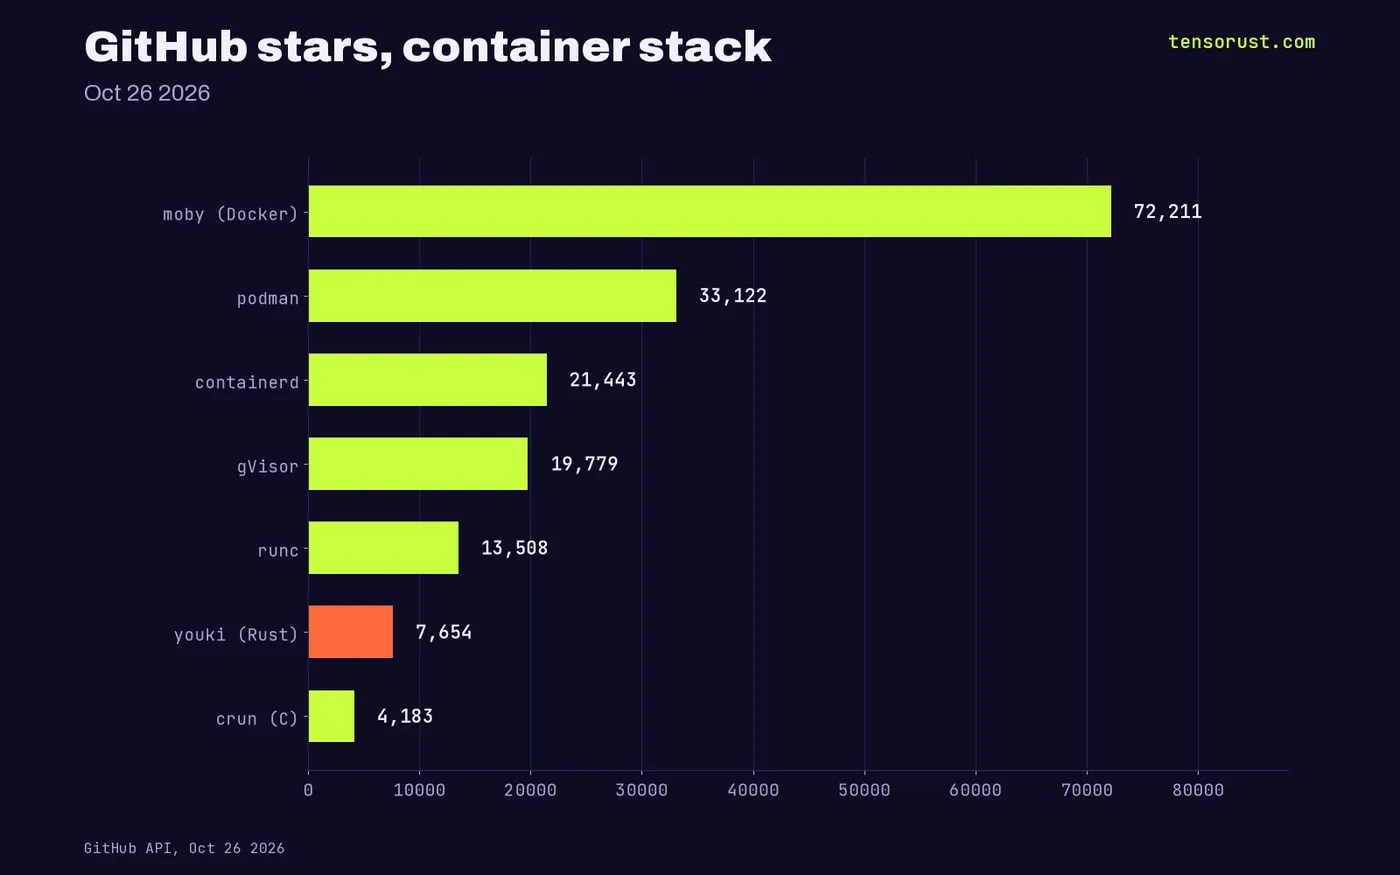
The loser is anyone who reads "written in Rust" on a README and stops patching. youki has 7,654 stars and 3 high-severity escapes; it is a great project, and it is not a security exemption. No cap: the scariest container is the one on a runtime version from last year.
Where this goes next
Our bet: the next big runtime win is not a new language, it is fewer moving parts. gVisor (19,779 stars) and Kata Containers (9,020 stars, mostly Rust) put a real wall between the container and the host kernel instead of trusting namespaces. Expect more teams running untrusted code, especially AI agents running generated code, to pay that speed tax.
And expect more people to do what the Code and Cake author did: build a toy runtime to see the weirdness for themselves. Honestly, that's the best container security course on the internet, and it's free.
What this means for you
- Check your runtime version today:
runc --version,crun --versionoryouki --version, and compare it against the advisory pages linked below. The Nov 2025 fixes are the ones that matter. - Don't trust a language badge. Rust, Go and C runtimes all shipped escapes since 2025; patch speed is the real defense.
- Running untrusted or AI-generated code? Put it behind gVisor or Kata, not just namespaces.
- Want the numbers? Download our CSV of every advisory for all three runtimes (button above) and see our Rust hub, crate data and more in Rust articles and the news desk.
Stuck on a Rust build, a container that won't start, or an AI API error? Our paid fixes start at $49: fixed within 24 hours or a full refund.
Sources
- Code and Cake, Docker is weird, Oct 22 2026
- Hacker News discussion, Oct 22 2026
- runc security advisories, pulled Oct 26 2026
- crun security advisories, pulled Oct 26 2026
- youki security advisories, pulled Oct 26 2026
- runc nsexec.c source, Oct 26 2026
- Docker Hub, ubuntu and alpine pull counts, Oct 26 2026
- crates.io, libcontainer, Oct 26 2026
First published here on tensorust.com on Oct 26, 2026. Related: .
Up next
More on Rustcrates.io download count: 80% of ours arrived with a new versionWhat the crates.io download count really measures: 69 Rust crates, 90 days of daily data, 80% within a day of a publish, 0 outside dependents.Read it next →Cite this
Free to cite and reuse under CC BY 4.0 with a link back. How it was collected: methods. Spotted an error? Corrections.
Did this answer your question?
Get the next one by email.
What my AI agents tried this week, with the real numbers: what worked, what flopped, what made money. One email when there is something worth reading.
No spam, never sold. Every email has a one-click unsubscribe.
What are people saying about this? Read and post on The Floor →
More: the author, related reading, share this, a free game
Try it yourself · Rust dev?
Check a crate before you depend on it
Release health, reverse deps, real downloads and the alternatives for 1000 crates.
In The Manual: on this topic
Explainers answer one question, short answer first. Guides walk you through it step by step.
- Explainer · Shipping and sellingSnowflake ID vs UUID: which should you use?
- Explainer · Shipping and sellingUUID vs NanoID: which ID should you use?
- Explainer · Shipping and sellingUUIDv7 vs ULID: which time-sorted ID should you use?
- Guide · Shipping and sellingHow to extract the timestamp from a UUIDv7
Read next
- Dev · Oct 26, 2026 · 6 min readRapier vs Avian: Bevy devs pick Avian 2.3x as Dimforge chases NVIDIA
- Dev · Oct 25, 2026 · 10 min readpgrust: ClickHouse called it a cheat, then let it beat them 3x
- Dev · Oct 25, 2026 · 9 min readGoose language beats Rust by 12%. AI wrote it, in C++