
By Matt Busel, who built the apps, crates and game he writes about · every number links to its source and every dataset is downloadable (methods) · corrections · featured in Kirino, gamebiz, This Week in Rust, New Mobile Life, By-Press
zip crate CVE: 77% of top Rust dependents can't get the 10.0 fix
On this page · 9 sections
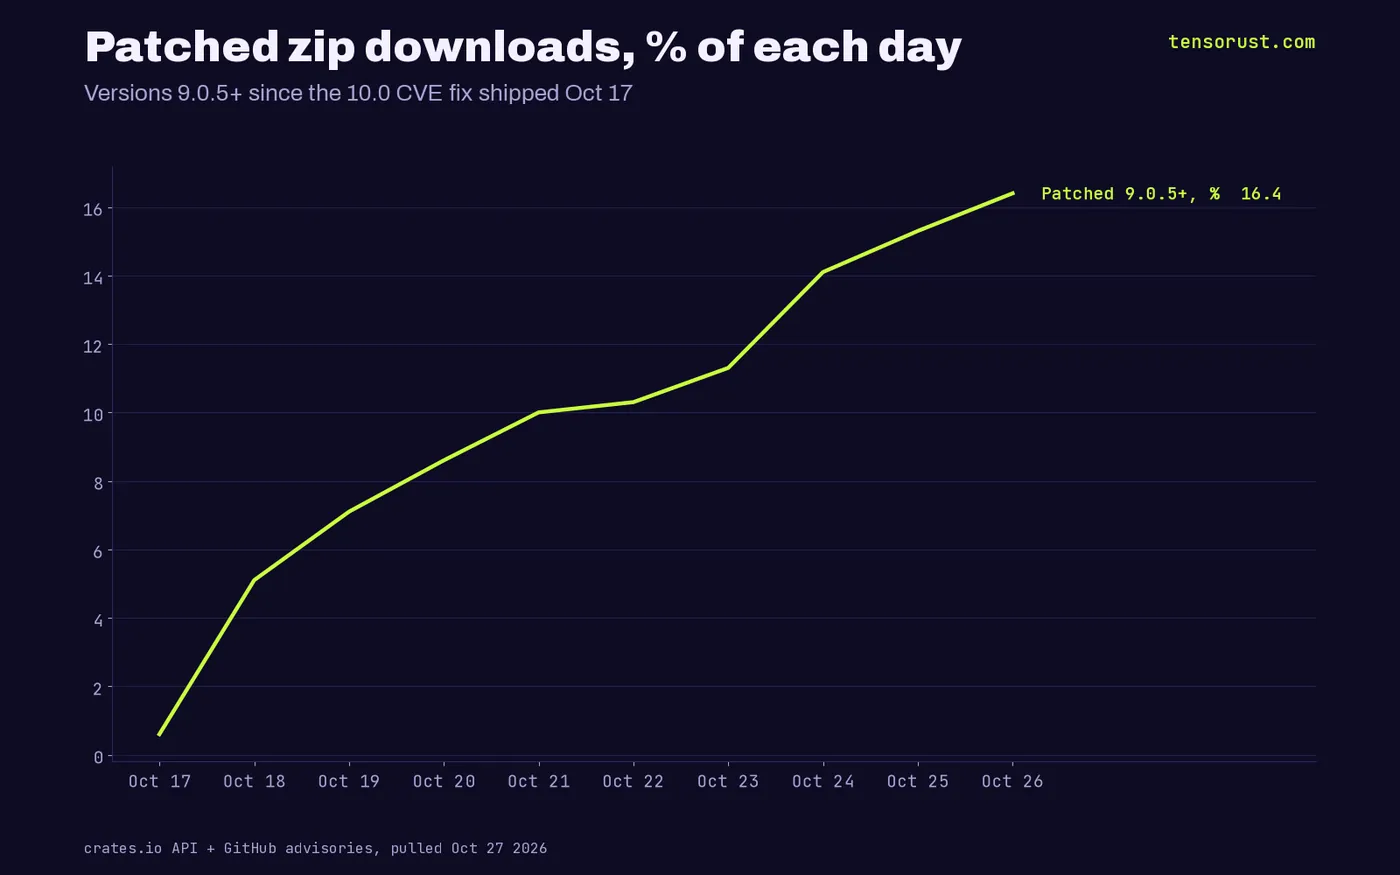
Short answer: The Rust zip crate shipped a fix for a critical "zip cloaking" bug (CVE-2026-115905) in version 9.0.5 on Oct 17, and r/rust is telling everyone to update. But we pulled the 300 most-downloaded crates that depend on zip, and 232 of them (77%) pin an older major version, so cargo update can never reach the fix. Ten days in, only 16.4% of daily zip downloads are a patched build.
TL;DR: The zip2 maintainers published 13 security advisories in 18 days this month: 1 critical, 6 high and 6 medium, and every fix landed only on the 9.x line. Of 13.85 million zip downloads from Oct 17 to Oct 26, just 1.41 million (10.2%) were 9.0.5 or newer. Hugging Face's candle-core, tauri-plugin-updater, tch, headless_chrome and docx-rs all still require a pre-9 zip in their current releases, so if you unzip anything a stranger sent you, check your own Cargo.lock tonight.
Key numbers
| What | Number | Source, checked Oct 27 2026 |
|---|---|---|
| zip advisories published Oct 9 to Oct 26 | 13 (1 critical, 6 high, 6 medium) | GitHub zip-rs/zip2 advisories |
| Top 300 dependents that cannot semver-update to 9.0.5 | 232 of 300 (77%) | crates.io reverse dependencies |
| Same, weighted by each dependent's downloads | 72% | crates.io API |
| Runtime (non dev, non build) dependents stuck | 194 of 251 | crates.io API |
| Patched share of zip downloads, Oct 17 to 26 | 10.2% (1.41M of 13.85M) | crates.io downloads API |
| Patched share on Oct 26 alone | 16.4% | crates.io downloads API |
| zip downloads, last 90 days | 91.7M | crates.io |
| Crates that depend on zip | 4,202 | crates.io API |
The fix exists. Most of Rust can't install it
The critical bug is a parser split. ZipArchive trusts the file names in the central directory at the end of the archive, while ZipStreamReader trusts the local headers in front of each file. Same zip, two different file lists.
The advisory spells out the attack: a scanner or upload gateway sees doc_report.pdf, the extractor writes cron_worker.sh. The reporter, ByGh00st, scored it 10.0. GitHub lists it as critical, affecting every version up to 9.0.4, patched in 9.0.5.
Here is the catch nobody in the "just update" thread mentions. Cargo follows semver: a crate that asks for zip = "^8.6.0" will happily take 8.6.1, but never 9.0.5. And there is no 8.6.1. Every one of the 13 fixes shipped on 9.x only.
232 of the top 300 are pinned to the past
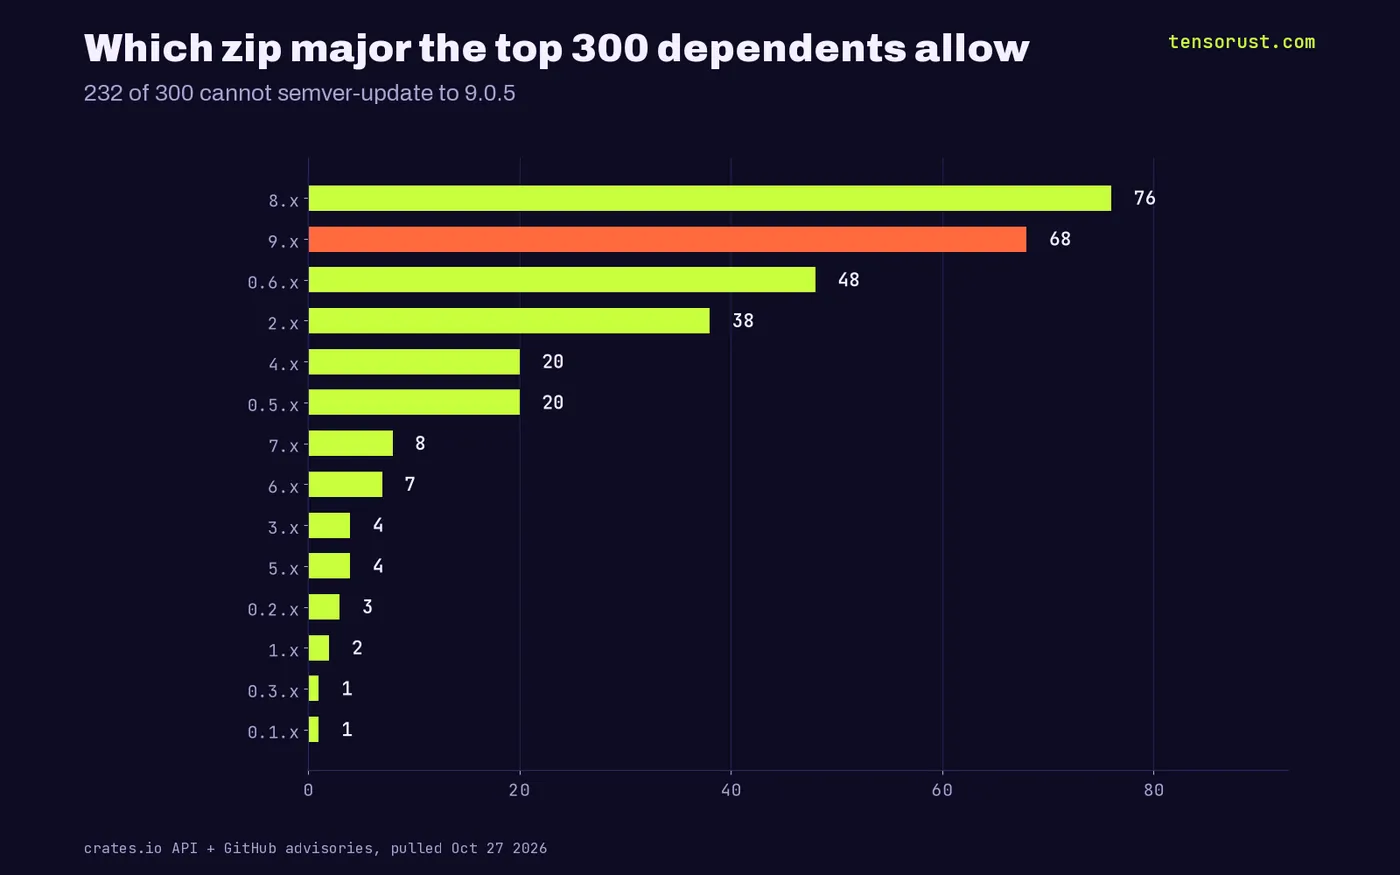
We pulled the 300 most-downloaded crates that list zip as a dependency and read the version requirement in each one's current release. Only 68 allow 9.x. The rest are spread across six older majors, with 76 on 8.x, 48 still on the ancient 0.6 line and 38 on 2.x.
Weight it by how much each dependent gets downloaded and it is still 72% stuck. Cut the dev and build dependencies (which mostly never touch an attacker's file) and 194 of 251 runtime dependents still can't get the fix.
This is not a "long tail of abandoned hobby crates" story. The biggest names are right at the top of the list.
The worst offenders, by name
- Hugging Face
candle-core0.11.0:zip ^8.6.0, a runtime dependency. Candle reads model and tensor files, many of them zip-based, pulled from the internet. 10.65M downloads. tauri-plugin-updater2.14.0:zip ^4. An auto-updater is the one piece of an app whose whole job is unpacking a downloaded archive. 13.2M downloads.tch0.26.0:zip ^0.6, the PyTorch bindings, on a major line from before 2023. 8.7M downloads.headless_chromeanddocx-rs:^8.6.0. A .docx file is a zip, so every document a user uploads goes through it.xwin(^8.0),grcov(^8.2),temporalio-sdk-core(^8.4), Sentry'ssymbolic-debuginfo(^7.2.0).
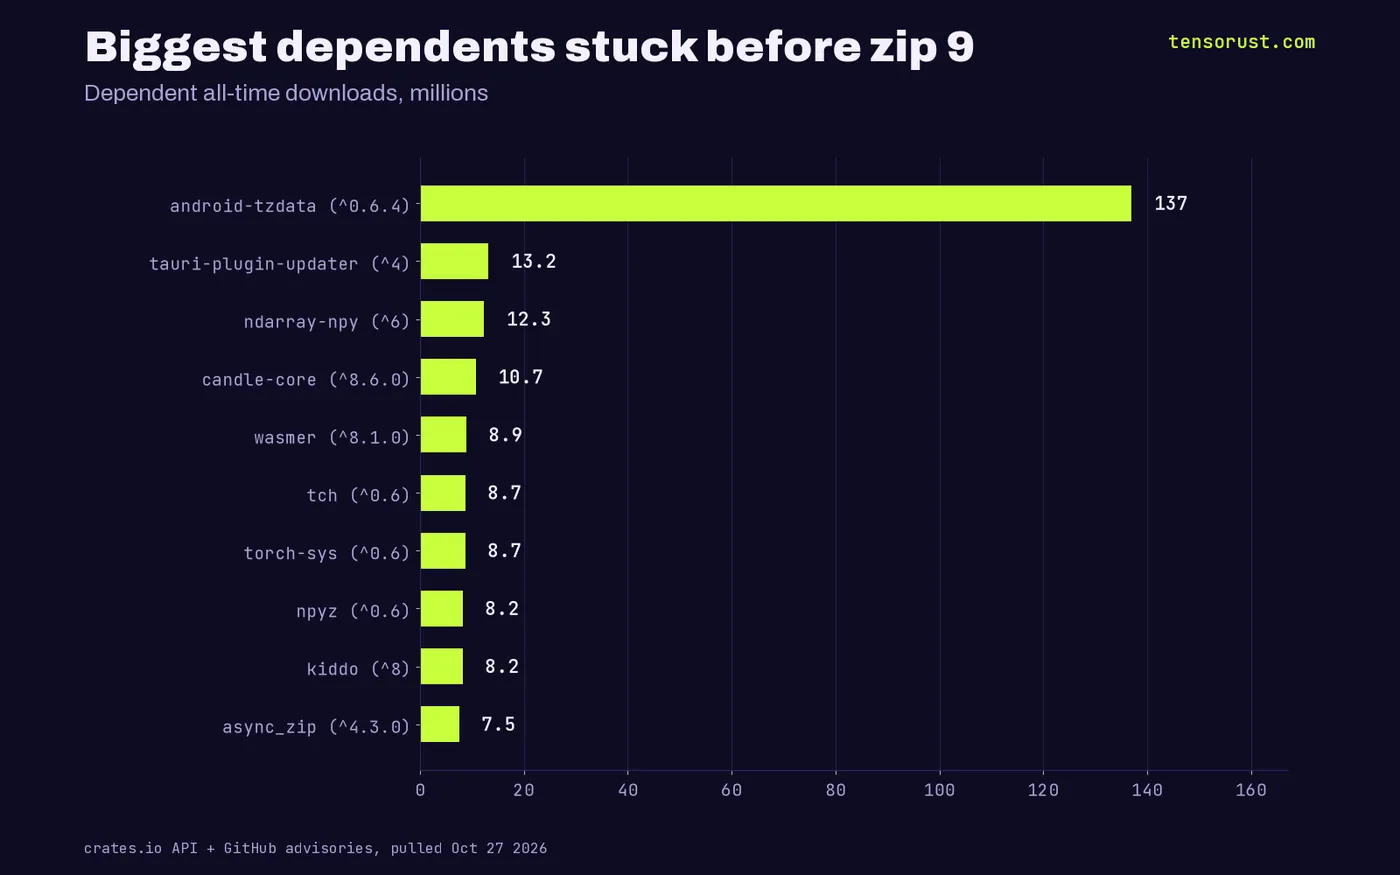
To be fair to them, the 9.0 bump landed Oct 9, eighteen days ago, and a major version can break APIs. But the advisories are public now, with exact reproduction steps, and the attacker reads the same GitHub page you do.
Thirteen advisories in eighteen days is the real story
Something changed in October. The zip2 repo had one advisory in all of 2025. Then 13 arrived between Oct 9 and Oct 26, credited to 12 different outside reporters, most of them hitting the same soft spot: symlinks and paths during extraction.
Our read: this is what AI-assisted bug hunting looks like when it points at a parser. Nobody has proven that is how these were found, but the pattern (many new reporters, same bug class, days apart) matches every other crate and package that got swarmed this year. Expect the same wave to hit tar, flate2 and every image decoder next.
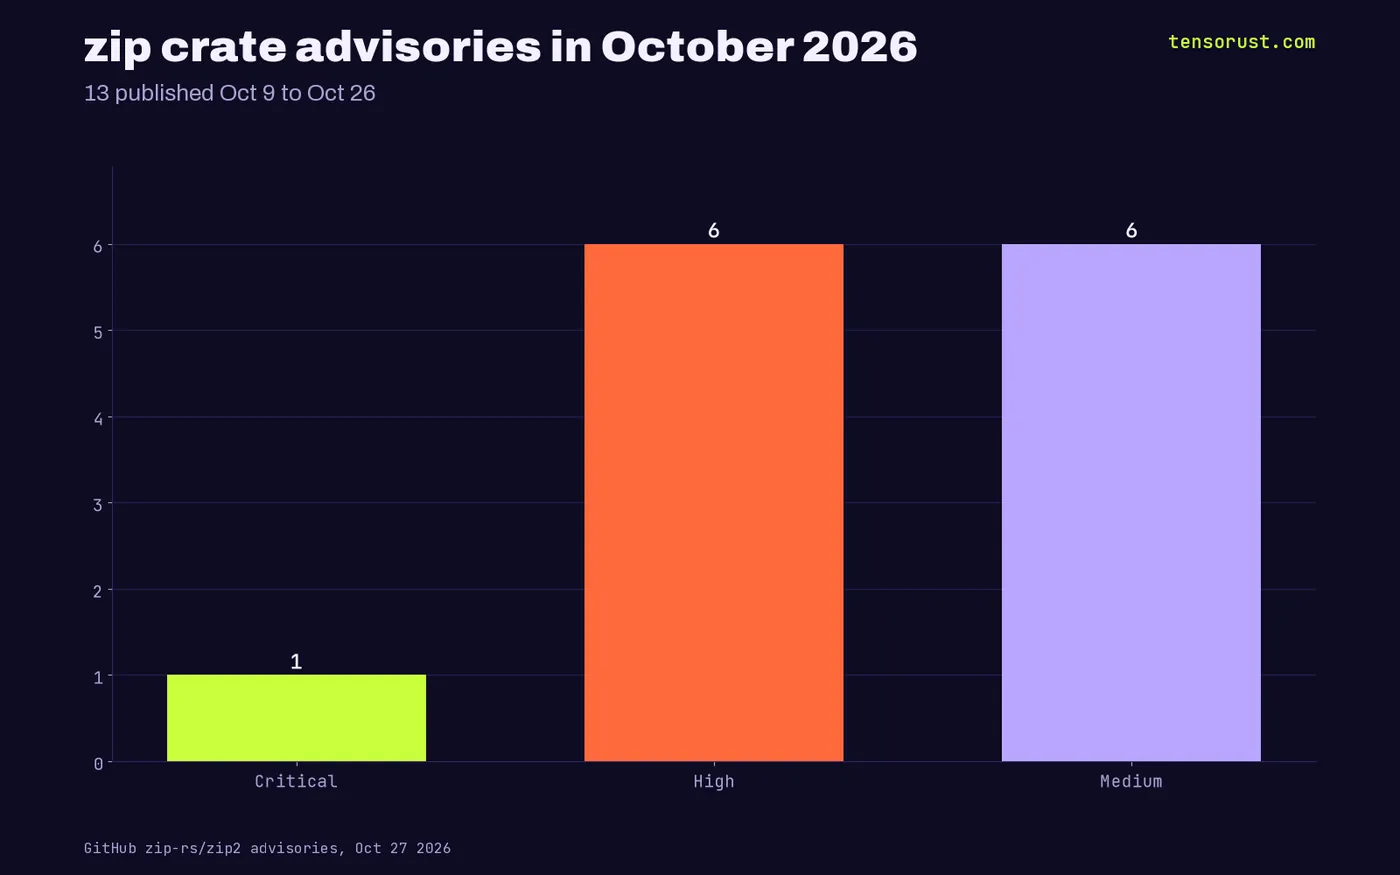
Lowkey the maintainers here are doing it right. Pr0methean, the zip2 maintainer, is credited on 8 of the 14 advisories and shipped nine releases in 17 days, 9.0.0 through 9.1.2. The bottleneck is the dependents.
Memory safety was never going to save you here
Every one of these bugs is in safe Rust. Path traversal, symlink escapes, a parser that believes the wrong header: the borrow checker does not care which file name you trust. We said the same about the Rust container runtime in our youki piece, and it is the same lesson as the Brotli fix that sat public for 236 days.
Rust wins on whole bug classes. It does not win on logic, and "written in Rust" on a README is not a security audit.
Who wins, who loses
Winners: anyone already on 9.x, plus the security scanners that get to flag 4,202 crates at once. Losers: every downstream app that pulls zip through a crate it does not control, because you cannot fix it without your dependency shipping a release first.
Our bet: within a month, at least one of the big names above ships a 9.x bump, and RustSec gets pressure to make cargo audit flag "your dependency is pinned below every fix" as its own warning. That warning should exist today.
What this means for you
Run cargo tree -i zip and look for any version below 9.0.5. If one of your direct dependencies pins it, send that crate a PR bumping to zip = "9"; if you can't wait, a [patch] won't cross majors, so vendor or fork. And if your app unzips files from users, do not ship until every path in that tree is 9.0.5 or newer.
The full list of 300 dependents, their requirement and whether they can update is in the data download below, so you (or your agent) can grep it in seconds. More on the ecosystem in our Rust hub, crate tracker and every Rust piece.
The limit here is time: the gap between a fix existing and your build running it. Today that gap is measured in weeks, and it is the only number in this story you control. Close it once by hand, then keep it closed: Crate Portfolio reads your Cargo.lock and reports the dependency health of every crate in it, and the monthly plan re-checks it as new advisories land, so the next zip-style wave shows up in your inbox instead of on Reddit.
Stuck on a dependency bump that breaks the build? Our paid fix gets your Rust build working on the patched crate within 24 hours, or a full refund.
Sources
- GitHub, zip-rs/zip2 security advisories (14 total, 13 in October), pulled Oct 27 2026
- GHSA-m665-v7pm-7grj, Dual-Header Inconsistencies (Zip Cloaking), CVE-2026-115905, Oct 17 2026
- crates.io, zip reverse dependencies API (top 300 by downloads), Oct 27 2026
- crates.io, zip daily downloads by version, Oct 27 2026
- r/rust, "10.0 critical CVE (RCE): update zip crate to 9.0.5", Oct 26 2026
First published here on tensorust.com on Oct 27, 2026. Related: .
Up next
More on RustOffline Rust builds: 17,527 downloads, almost nobody is shutdown-readyOffline Rust builds after Iran's 88-day blackout: 6 offline cargo tools got 17,527 downloads in 90 days, cargo-chef got 1.2M. How to vendor in an afternoon.Read it next →Cite this
Free to cite and reuse under CC BY 4.0 with a link back. How it was collected: methods. Spotted an error? Corrections.
Did this answer your question?
Get the next one by email.
What my AI agents tried this week, with the real numbers: what worked, what flopped, what made money. One email when there is something worth reading.
No spam, never sold. Every email has a one-click unsubscribe.
What are people saying about this? Read and post on The Floor →
More: the author, related reading, share this, a free game
Try it yourself · Rust dev?
Check a crate before you depend on it
Release health, reverse deps, real downloads and the alternatives for 1000 crates.
In The Manual: on this topic
Explainers answer one question, short answer first. Guides walk you through it step by step.
- Guide · Rust and cratesHow to check your Cargo.lock for vulnerabilities with cargo audit
- Guide · Rust and cratesHow to vendor Rust dependencies with cargo vendor for offline builds
- Explainer · Shipping and sellingSnowflake ID vs UUID: which should you use?
- Explainer · Shipping and sellingUUID vs NanoID: which ID should you use?
Read next
- Dev · Oct 26, 2026 · 6 min readOpen source is an unpaid utility, and the EU just sent the bill
- Dev · Oct 26, 2026 · 6 min readOffline Rust builds: 17,527 downloads, almost nobody is shutdown-ready
- Dev · Oct 26, 2026 · 6 min readRust PDF crates: PaperPilot hit HN, Python pulls 40x the downloads
.jpg)