By Matt Busel, who built the apps, crates and game he writes about · every number links to its source and every dataset is downloadable (methods) · corrections · featured in Kirino, gamebiz, This Week in Rust, New Mobile Life, By-Press
tokio-tar has no TARmageddon fix. Its downloads rose 58% anyway
On this page · 9 sections
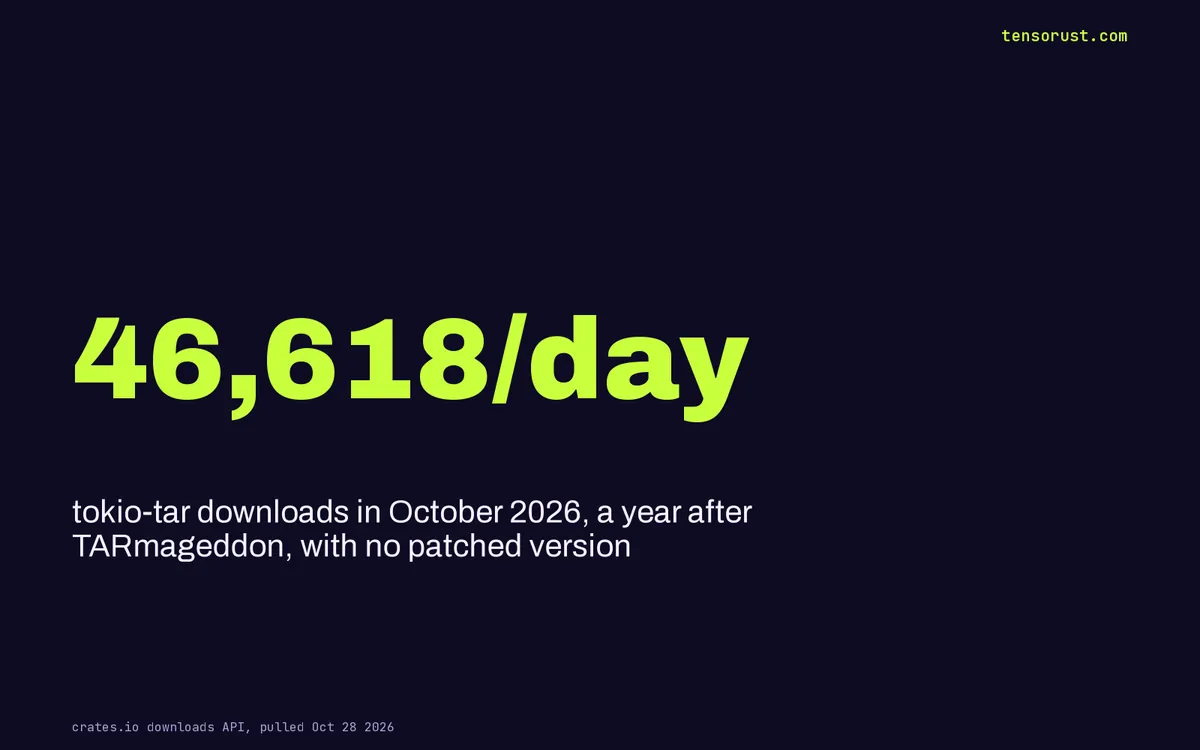
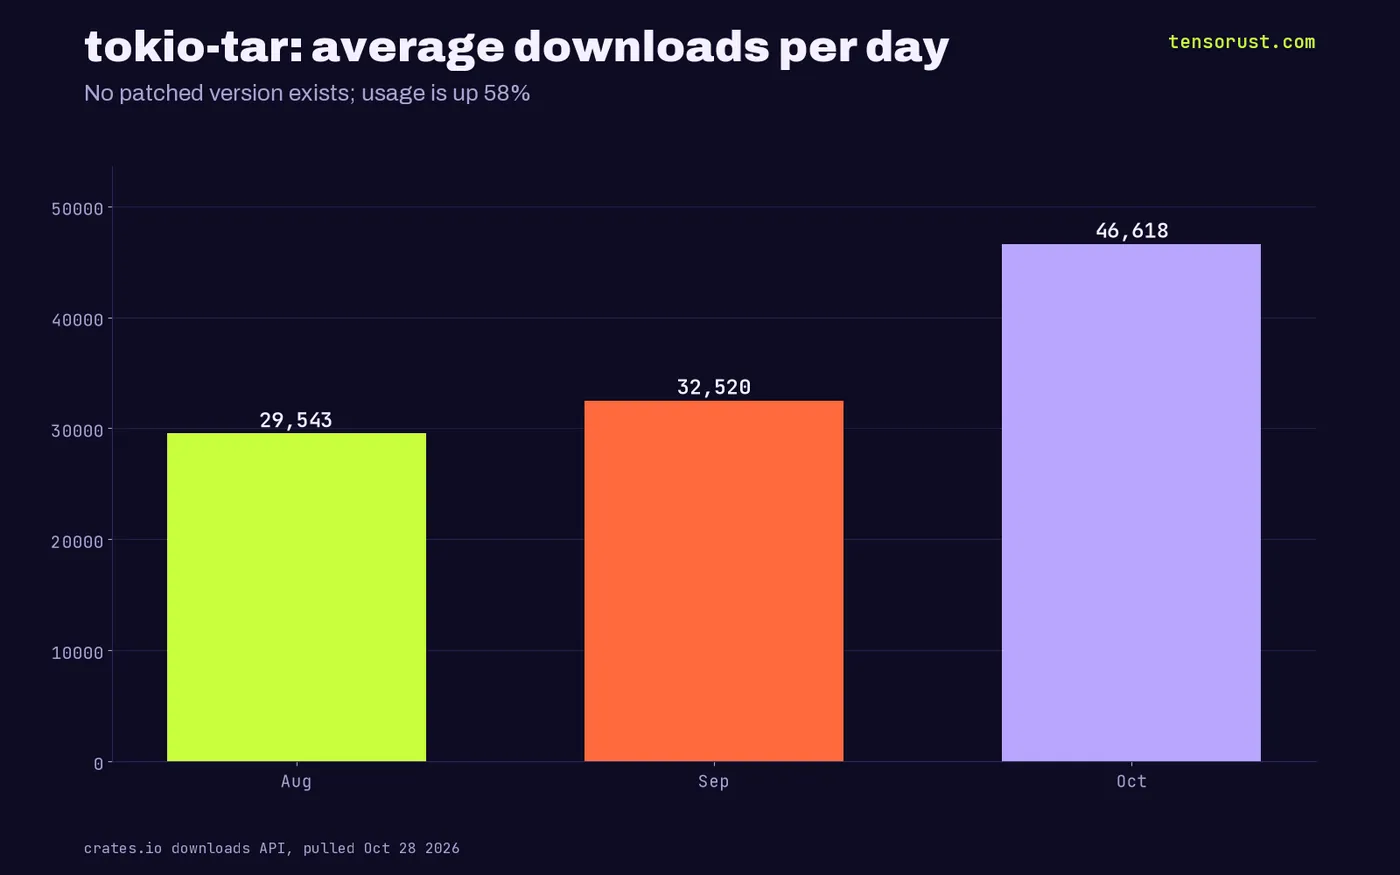
Short answer: tokio-tar still has no fixed version for CVE-2025-62518 (TARmageddon), and Rust builds pulled it 46,618 times a day in October 2026, up 58% from August. Matrix.org's opa-wasm shipped a new release on October 27 that still depends on it. The fix exists one crate over; the ecosystem is just not taking it.
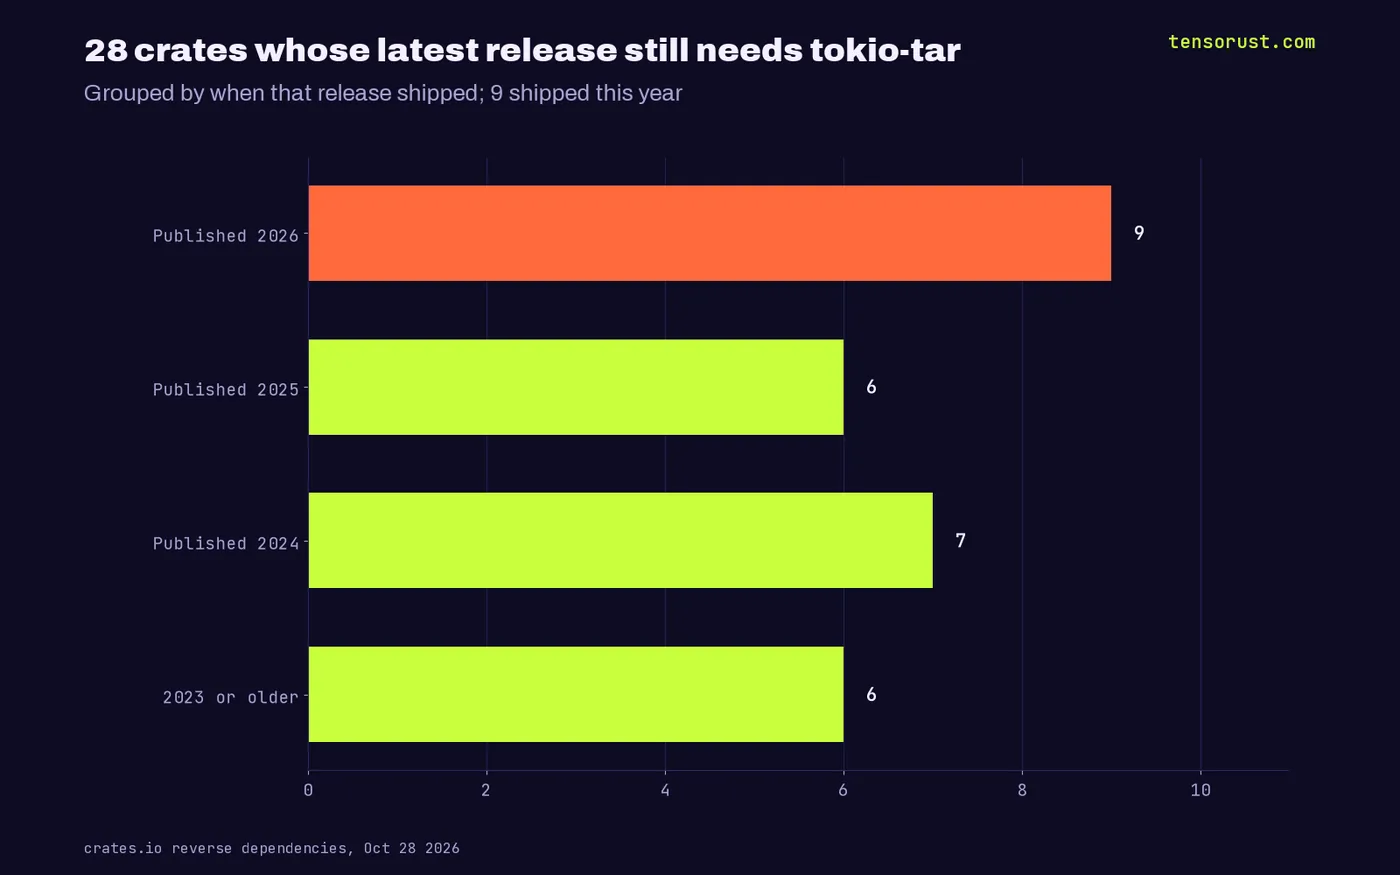
TL;DR: We pulled 90 days of crates.io download data: tokio-tar averaged 29,543 downloads a day in August, 32,520 in September and 46,618 in October, with a single-day peak of 138,704 on October 22. The RustSec advisory (RUSTSEC-2025-0111) lists every version as affected with no fixed release, because the maintainer is gone. Of the 28 crates whose latest release still requires tokio-tar, 9 shipped that release in 2026, so new code is still choosing the broken crate a full year after the headlines.
Key numbers
| What | Number | Source, checked Oct 28 2026 |
|---|---|---|
| tokio-tar downloads per day, Oct 2026 (Oct 1-27) | 46,618 | crates.io |
| Same, Aug 2026 | 29,543 | crates.io |
| Peak day | 138,704 (Oct 22) | crates.io |
| tokio-tar total downloads | 19,268,826 | crates.io |
| Last tokio-tar release | 0.3.1, July 14 2023 | crates.io |
| Fixed versions of tokio-tar | 0 | RustSec |
| Crates whose latest release requires it | 28 (9 released in 2026) | crates.io |
| astral-tokio-tar (patched fork) per day, Oct 2026 | 178,717 | crates.io |
The bug got the headlines in 2025. The usage never stopped
In October 2025, Edera disclosed TARmageddon: a tar parsing flaw where a crafted PAX header makes the parser skip into the wrong spot, so an attacker can smuggle extra files into what looks like a clean archive. Plain version: the archive you inspected is not the archive you unpacked.
The coverage at the time (BleepingComputer, The Hacker News) said the same thing: tokio-tar is abandoned, there will be no patch, move to Astral's fork. Then everybody moved on to the next CVE.
We went back a year later and pulled the numbers. Nobody had.
Downloads went up, not down
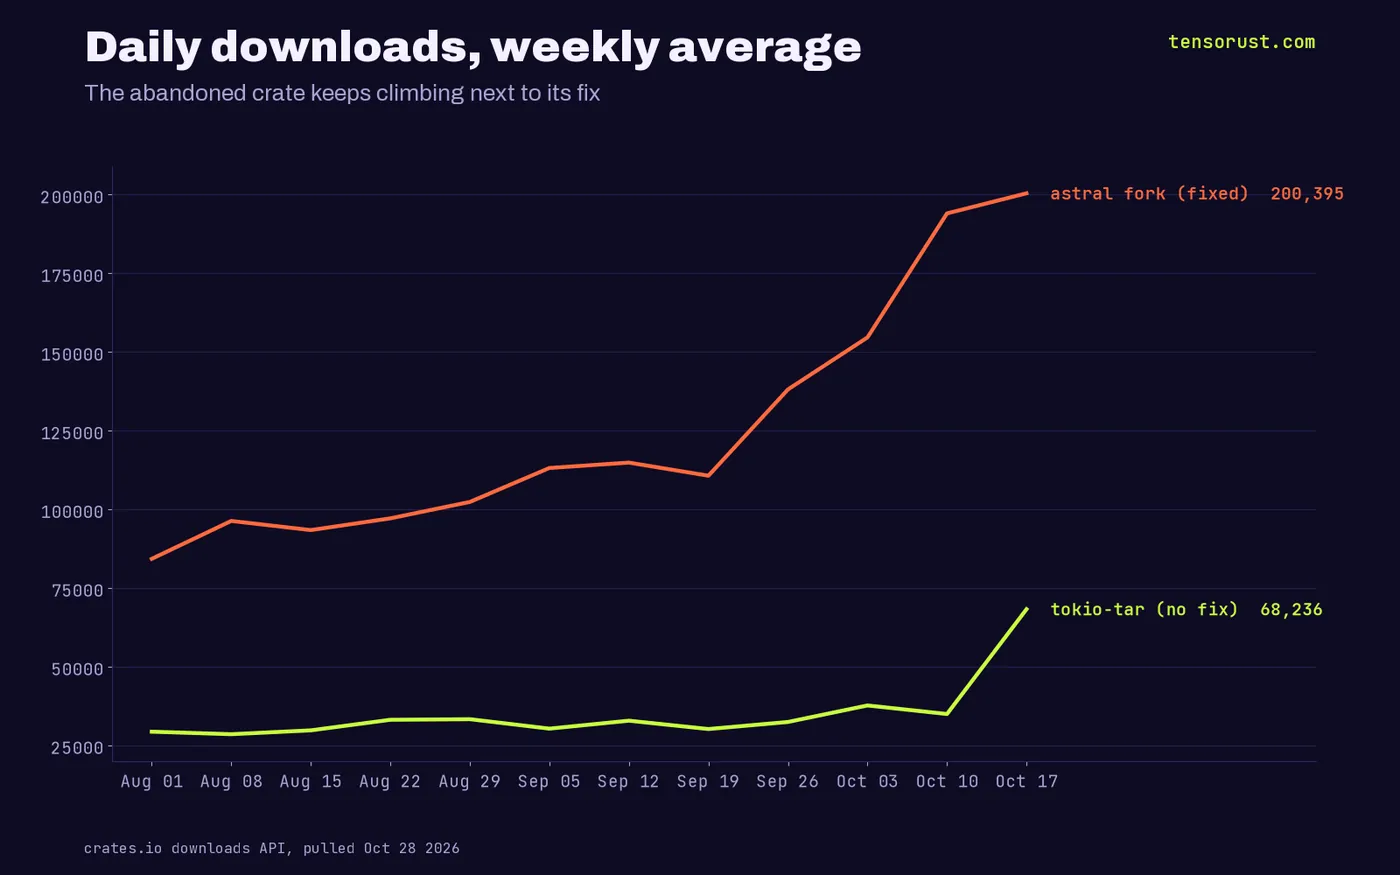
A dead crate with a public high-severity bug should be fading. tokio-tar is doing the opposite. Daily downloads rose from 29,543 in August to 46,618 in October, and the week starting October 17 averaged 68,236 a day.
The fork is growing faster, to be fair to the people who did migrate: astral-tokio-tar went from 91,081 a day in August to 178,717 in October. So the share of builds on the unpatched crate dipped from about 24% to about 21%. That is progress at a pace that would finish the migration sometime around never.
Downloads are CI runs and fresh builds, not unique humans, so treat them as a measure of how often the crate lands in a build, not how many teams use it. A spike like October 22 usually means one big project's pipeline is rebuilding a lot. Either way, every one of those builds is compiling a parser with a known smuggling bug.
New code is still picking the broken crate
The scarier number is not the download curve. It is who is still choosing it. Of the 28 crates whose current release requires tokio-tar, 9 published that release in 2026, after the advisory was public and after cargo audit started flagging it.
- opa-wasm 0.3.4 (matrix-org/rust-opa-wasm): released October 27 2026, requires tokio-tar ^0.3. It is the policy engine runner from the Matrix.org Foundation, with 14,364 downloads in the last 90 days.
- libpkgx 0.9.0 (pkgx, the package runner from Homebrew's creator Max Howell): July 22 2026. A package manager is the exact place an archive smuggling bug matters.
- pesde 0.7.4 (Luau/Roblox package manager) and lighty-core 26.9.3 (Minecraft launcher library): both September 9 2026. Again: tools whose whole job is unpacking archives from the internet.
- wash-cli 0.39.0 from wasmCloud, named in the original 2025 coverage, still lists tokio-tar on its latest crates.io release (February 2025).
We are not saying any of these projects has been exploited. We are saying the fix has been one line in Cargo.toml for a year, and package managers are still shipping without it. Our read: Rust's "memory safe" reputation made people treat the whole language as safe, and logic bugs like this one ride along unnoticed.
How the smuggling works, step by step
A tar file is a list of entries, each with a header that says how big the file body is. PAX headers are an extension that can override that size, for example for files over 8 GB.
- The attacker writes a PAX header that says the next file is one size, while the plain ustar header says another (often zero).
- tokio-tar reads the wrong one and advances by the wrong number of bytes.
- It lands in the middle of what a correct parser treats as file content, and reads attacker data there as brand new entries.
- A scanner or a different tar tool sees one set of files; tokio-tar unpacks another. That gap is how you swap a config file or a build script inside a package that passed review.
Edera rated it 8.1 out of 10. Nothing about Rust's borrow checker stops this. It is a logic bug, and memory safety does not cover logic.
Why a dead crate keeps growing
Most of those downloads are not people typing tokio-tar into Cargo.toml. They are transitive: a crate you depend on depends on it, and every fresh CI runner without a warm cache fetches it again. As Rust adoption grows, every old pin grows with it.
That is the real mechanism. Abandoned crates do not die; they get carried. The only thing that stops it is a human in the middle of the chain changing one line, and for this crate, 28 projects at the top of the chain have not.
Who is to blame (it is not one maintainer)
It is easy to blame the original author for walking away. That is the wrong target. Nobody owes free maintenance forever. The failure is that crates.io still serves tokio-tar with no warning on the page, cargo does not block a dependency with an unfixed critical advisory by default, and big downstream projects let a transitive pin sit for twelve months.
The Rust ecosystem has the data to fix this. RustSec knows the crate is unfixable. crates.io knows who depends on it. Connecting those two, as we just did in an afternoon, is the whole job. More on this pattern in our zip crate CVE breakdown, the Rust hub and our crate tracker.
What this means for you
Run cargo tree -i tokio-tar in every Rust repo you own today. If anything shows up, swap it for astral-tokio-tar = "0.7" (a maintained fork from Astral, the uv team; the fix landed in 0.5.6), or open an issue on the upstream crate that drags it in. Add cargo audit or cargo deny check advisories to CI so the next abandoned crate fails the build instead of a headline. Download our full daily data and the list of 28 dependents below, and check whether your stack is on it.
If the swap breaks your build and you would rather not spend the evening on it, our paid Rust fix gets it done: fixed within 24 hours or a full refund.
Sources
- crates.io, tokio-tar downloads and reverse dependencies, pulled Oct 28 2026
- crates.io, astral-tokio-tar downloads, pulled Oct 28 2026
- RustSec, RUSTSEC-2025-0111 (tokio-tar, no fixed version), checked Oct 28 2026
- RustSec, RUSTSEC-2025-0110 (astral-tokio-tar, fixed in 0.5.6), checked Oct 28 2026
- Edera, TARmageddon (CVE-2025-62518), Oct 2025
- BleepingComputer, TARmageddon flaw in abandoned Rust library, Oct 2025
First published here on tensorust.com on Oct 28, 2026. Related: .
Up next
More on RustWild linker 0.11: links Chromium 5x faster than LLD, now does WasmWild 0.11, a Rust linker, beat Mold 3.0 in 35 of 35 benchmarks and LLD in 35 of 36. Linking Chromium, LLD takes 5.3x as long. Now does Wasm too.Read it next →Cite this
Free to cite and reuse under CC BY 4.0 with a link back. How it was collected: methods. Spotted an error? Corrections.
Did this answer your question?
Get the next one by email.
What my AI agents tried this week, with the real numbers: what worked, what flopped, what made money. One email when there is something worth reading.
No spam, never sold. Every email has a one-click unsubscribe.
What are people saying about this? Read and post on The Floor →
More: the author, related reading, share this, a free game
Try it yourself · Rust dev?
Check a crate before you depend on it
Release health, reverse deps, real downloads and the alternatives for 1329 crates.
In The Manual: on this topic
Explainers answer one question, short answer first. Guides walk you through it step by step.
- Guide · Rust and cratesHow to check your Cargo.lock for vulnerabilities with cargo audit
- Guide · Rust and cratesHow to vendor Rust dependencies with cargo vendor for offline builds
- Explainer · Shipping and sellingSnowflake ID vs UUID: which should you use?
- Explainer · Shipping and sellingUUID vs NanoID: which ID should you use?
Read next
- Dev · Oct 27, 2026 · 6 min readWild linker 0.11: links Chromium 5x faster than LLD, now does Wasm
- Dev · Oct 27, 2026 · 5 min readsystemd lets Rust in: 0 of its last 14 CVEs were memory bugs
- Dev · Oct 27, 2026 · 6 min readzip crate CVE: 77% of top Rust dependents can't get the 10.0 fix